Hiring guide
Penetration testing renewal: deciding what next year looks like
Penetration testing renewal comes around every year for most organizations. It is easy to repeat last year's order. However, the estate has changed, and so may the people asking for evidence, so the renewal deserves a short review.
- Signed scope before testing
- Fixed price agreed in writing
- OWASP and PTES methods
Why penetration testing renewal is a decision
Last year's scope described last year's estate. New products, cloud moves and acquisitions all change what matters. So a copied scope can leave important systems out.
In addition, customers and auditors change their requests. A renewal is the moment to check what they now expect.
What to review before penetration testing renewal
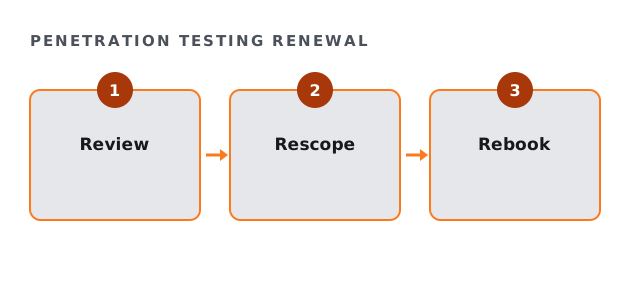
Start with last year's file: scope, report, retest and lessons. Then list what changed since. Finally, check upcoming deadlines that need evidence.
Because those three inputs define the new scope, the review takes an hour rather than a week.
| Input | Question |
|---|---|
| Last year's scope | What did it cover and leave out? |
| Report and retest | Which issues returned? |
| Changes since | What is new in the estate? |
| Deadlines | Who needs evidence, and when? |
| The firm | Keep, rotate or replace? |
Penetration testing renewal checklist
Tick what your review already covers.
Your result appears here as you tick, so you can see what is still open.
Same firm or a new one
Staying with a firm saves onboarding time, because it knows the estate. However, a fresh firm brings a new view. Some organizations rotate every few years for that reason.
So decide on evidence. Did the last engagement meet its dates, produce usable findings and close with a clean retest?
Timing the penetration testing renewal
Work back from the evidence deadline. Allow for lead time, the testing window, the report, fixes and the retest. Then add a margin.
As a result, the new report arrives before anyone asks for it, rather than after.
Paperwork for penetration testing renewal
If an agreement already exists, a new scope may be enough. However, authorization is never carried over. Each system owner signs again for the new scope.
Also update contacts. People move roles, and last year's operations contact may no longer be reachable.
Renewing with us
Send last year's scope and what changed. We reply with a written scope, and testing begins within 48 hours of the new authorization.
Full engagements run from $35,000 to $120,000, and the floor is $25,000. The bounded Focused Exposure Review starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days. One fixed number is agreed after the scoping brief, and it never moves during the project. The method follows the Penetration Testing Execution Standard.
Penetration testing renewal questions
When should penetration testing renewal start?
Work back from your evidence deadline, with a margin.
Can we reuse last year's scope for penetration testing renewal?
As a starting point only. Update it for what changed.
Is authorization carried over?
No. Each owner signs again for the new scope.
Should we change firms at penetration testing renewal?
Decide on evidence from the last engagement.
Related guides
Start your penetration testing renewal
Send last year's scope and what changed. We reply with a written scope and one fixed number.
Get a fixed price