Hiring guide
What a penetration testing SLA should promise in writing
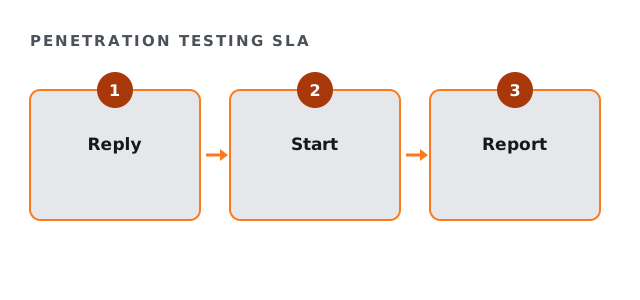
A penetration testing SLA is the service level part of the agreement. It turns vague promises into dates. So instead of soon, you get a reply time, a start date, a report day and a retest window.
- Signed scope before testing
- Fixed price agreed in writing
- OWASP and PTES methods
Why a penetration testing SLA matters
Most delays in testing are not technical. They come from slow replies, late starts and reports that arrive weeks after the window closed. Meanwhile, your deadline does not move.
Therefore put the key dates in writing. Then everyone can plan around them, including the auditor or customer waiting for evidence.
The dates in a penetration testing SLA
A useful agreement covers five moments. Each one should be a number of days or hours, not a description.
Also agree how dates shift if your side is late. For example, if access arrives two days late, the report date moves by two days.
| Moment | What to agree |
|---|---|
| Reply to a brief | A set number of business days |
| Start of testing | Hours or days after authorization |
| Urgent findings | Reported at once, not held for the report |
| Report delivery | A fixed day after the window closes |
| Retest | A window after your fixes are in |
Penetration testing SLA checklist
Tick each date your agreement already sets.
Your result appears here as you tick, so you can see what is still open.
Urgent findings in the penetration testing SLA
Some findings cannot wait for the report. A serious issue should be reported to your named contact as soon as it is confirmed.
So write that rule into the agreement, with the contact and the route. As a result, nobody hesitates during the window.
Checking the penetration testing SLA after the work
When the engagement closes, compare each date with what happened. If one slipped, ask why in writing.
Because the record is simple, it also helps next year. A firm that met every date has earned some trust.
What an SLA cannot fix
Dates do not create quality. A report delivered on time can still be thin. Therefore pair the service levels with a clear description of the deliverables.
Similarly, an SLA cannot make your own side faster. Access, contacts and approvals are still your part.
Our dates
A senior principal replies within one business day. Testing begins within 48 hours of authorization, and the report and debrief follow, with a free retest once your fixes are applied.
Full engagements run from $35,000 to $120,000, and the floor is $25,000. The bounded Focused Exposure Review starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days. One fixed number is agreed after the scoping brief, and it never moves during the project. The method follows the Penetration Testing Execution Standard.
Penetration testing SLA questions
What should a penetration testing SLA include?
Reply time, start date, urgent reporting, report day and retest window.
Do penetration testing SLA dates move if we are late?
They should move by the same amount, and the agreement should say so.
Are urgent findings covered?
They should be reported at once to a named contact.
Does a penetration testing SLA cover quality?
No. Describe the deliverables separately.
Related guides
Ask for our penetration testing SLA
Send a short brief with your deadline. We reply with a written scope, our dates and one fixed number.
Get a fixed price