Hiring guide
Penetration test sign off: closing the engagement properly
Penetration test sign off is the last signature in the engagement. It says the work was delivered as agreed. So before signing, check the deliverables, the retest, any open exceptions and what happens to your data.
- Signed scope before testing
- Fixed price agreed in writing
- OWASP and PTES methods
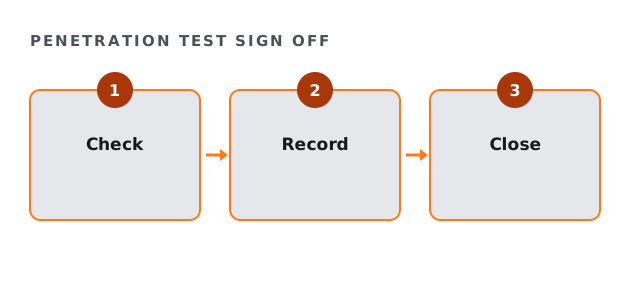
Why penetration test sign off matters
Without a formal close, engagements drift. Questions stay open, final invoices wait and nobody confirms that data was destroyed. A short sign-off ends all of that.
In addition, auditors sometimes ask when the work closed. A signed record answers that in one line.
What to check before penetration test sign off
Compare the deliverables with the scope. Each one promised should exist and be usable. Then confirm the retest result.
Also ask for written confirmation of data destruction. Because the report lists your weaknesses, copies should not survive the engagement.
| Item | Check |
|---|---|
| Findings report | Delivered and matches the scope |
| Business risk summary | Readable by your board |
| Remediation plan | Ordered by risk and effort |
| Debrief | Held, and questions answered in writing |
| Retest | Completed, with results recorded |
| Data destruction | Confirmed in writing |
Penetration test sign off checklist
Tick each item before you sign.
Your result appears here as you tick, so you can see what is still open.
Open findings at penetration test sign off
Not every finding is fixed by the end. That is normal. However, each open item should have an owner, a date or a written risk decision.
So sign-off closes the engagement, not the risk. The open list moves into your own tracking.
Who signs
Usually the security lead who owned the project. In larger organizations, the sponsor may countersign.
Then file the sign-off with the scope, authorization, report and retest. As a result, the whole engagement sits in one record.
When to delay penetration test sign off
Delay it if a deliverable is missing or a question is unanswered. Also delay it if the retest has not happened yet, unless you agreed to close without one.
Because the final invoice may depend on sign-off, the agreement should state the conditions clearly.
What we deliver before you sign
Findings report, business risk summary, prioritized remediation plan, written debrief and a free retest once you have applied the fixes. Zero client findings are retained after delivery.
Full engagements run from $35,000 to $120,000, and the floor is $25,000. The bounded Focused Exposure Review starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days. One fixed number is agreed after the scoping brief, and it never moves during the project. The method follows the Penetration Testing Execution Standard.
Penetration test sign off questions
Who gives penetration test sign off?
Usually the security lead, sometimes countersigned by the sponsor.
Must every finding be fixed before penetration test sign off?
No. Open items need an owner, a date or a written risk decision.
What if a deliverable is missing?
Delay sign-off until it arrives.
Where does the penetration test sign off record go?
In one file with the scope, authorization, report and retest.
Related guides
Plan penetration test sign off from day one
Send a short brief. We reply with a written scope that lists every deliverable, and one fixed number.
Get a fixed price